Card Testing Fraud: What It is and How to Stop The Attacks


Card testing fraud is when criminals use bots to run stolen card numbers through an online checkout to find out which ones still work. It’s a growing threat in eCommerce. Besides costing you money, it can damage your standing with your payment processor and, since 2025, with Visa’s fraud monitoring program.
In this guide, you’ll learn what card testing fraud is, how attacks happen, how to spot one, and how to protect your store from being targeted.
What is Card Testing Fraud?
Card testing fraud (also called carding or an enumeration attack) is when cybercriminals use stolen credit card numbers to check whether the cards still work. They usually run small or $0 transactions, or just failed attempts, on websites without strong bot and fraud protection.
Once they find a valid card, they use it for bigger purchases or sell it on the dark web. That’s why this type of ecommer frauds is often an early warning sign of bigger attacks.
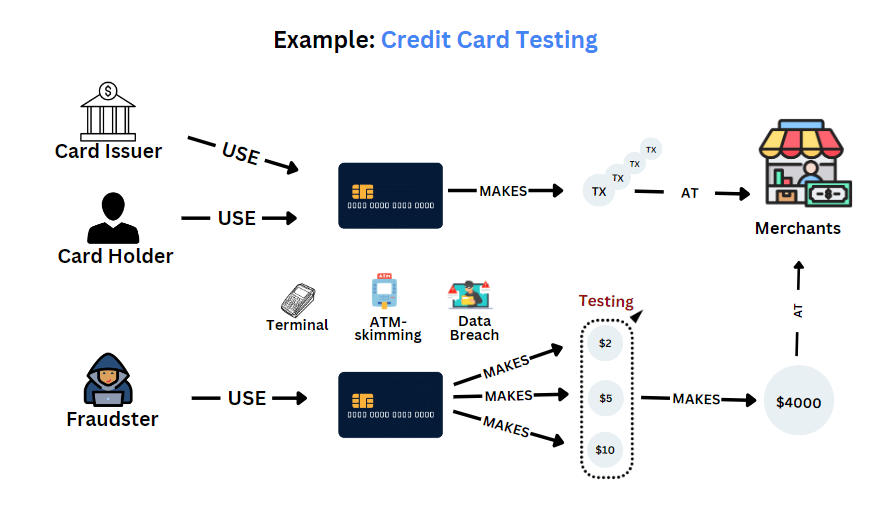
How Do Card Testing Attacks Work?
Card testing attacks are almost always automated and fast, which makes them hard to spot until the damage is done. Here’s how they typically unfold.
Cybercriminals collect stolen credit card data
Attackers get card details from data breaches, phishing schemes or dark-web marketplaces. They don’t know which of these cards are still active.
Example: An attacker buys a list of thousands of stolen card numbers for a few dollars, with no idea how many still work.
Attackers deploy bots or scripts to test cards
Attackers use bots or scripts to submit the cards one after another. Many of these bots skip your storefront entirely and open the checkout link directly, so protections on your store pages never see them. They usually try very small amounts, from $0 to a few dollars, to avoid fraud alerts.
Example: a Shopify store with no checkout protection gets 500 checkout attempts in 10 minutes, all for a $0.99 sticker.
Verified cards are marked and exploited
If a test goes through, the card is marked as “live.” The attacker then uses it for big-ticket purchases elsewhere or resells it at a higher price. Meanwhile, your store is left with suspicious charges, possible chargebacks and a pile of fake checkouts.
Your business pays the price
Card testing doesn’t just cost you money, it hurts your reputation. Payment processors may charge more per transaction or flag your store as high-risk. If customers notice strange activity tied to your store, they could lose trust and stop buying altogether.
Why Should You Care about Card Testing Fraud?
Card testing might seem harmless at first, after all, no products are actually stolen. But the hidden costs add up fast. Every failed transaction still incurs processing fees, and if hundreds of test attempts hit your store, that’s real money lost. Worse, if those attempts lead to chargebacks from cardholders who never authorized them, your chargeback rate can spike. That damages your standing with payment providers.
Eventually, your store could be labeled as high-risk or even get banned from platforms like Stripe or PayPal. And once you lose access to trusted payment gateways, recovering customer trust or even resuming operations becomes an uphill battle.
- Fees. Depending on your payment provider, failed attempts can still cost you. Some gateways charge per authorization attempt, and some fraud screening tools bill per transaction they review.
- Chargebacks. When a test charge goes through, the real cardholder often disputes it. Even small disputes raise your chargeback rate.
- Card-network penalties. On April 1, 2025, Visa merged its fraud and dispute programs into the Visa Acquirer Monitoring Program (VAMP), and enforcement began on October 1, 2025. VAMP adds an enumeration ratio that tracks card-testing attempts specifically. Declined attempts count too, so a store can be flagged because of attack volume alone. Merchants become eligible once they reach 300,000 enumerated transactions, and an enumeration ratio of 20% or more is treated as excessive.
- Payment account risk. Too many disputes or suspicious attempts can lead your processor to label your store high-risk, hold payouts, add reserves, or close your account.
- Polluted data. Thousands of fake checkouts bury your real abandoned carts and distort your conversion numbers.
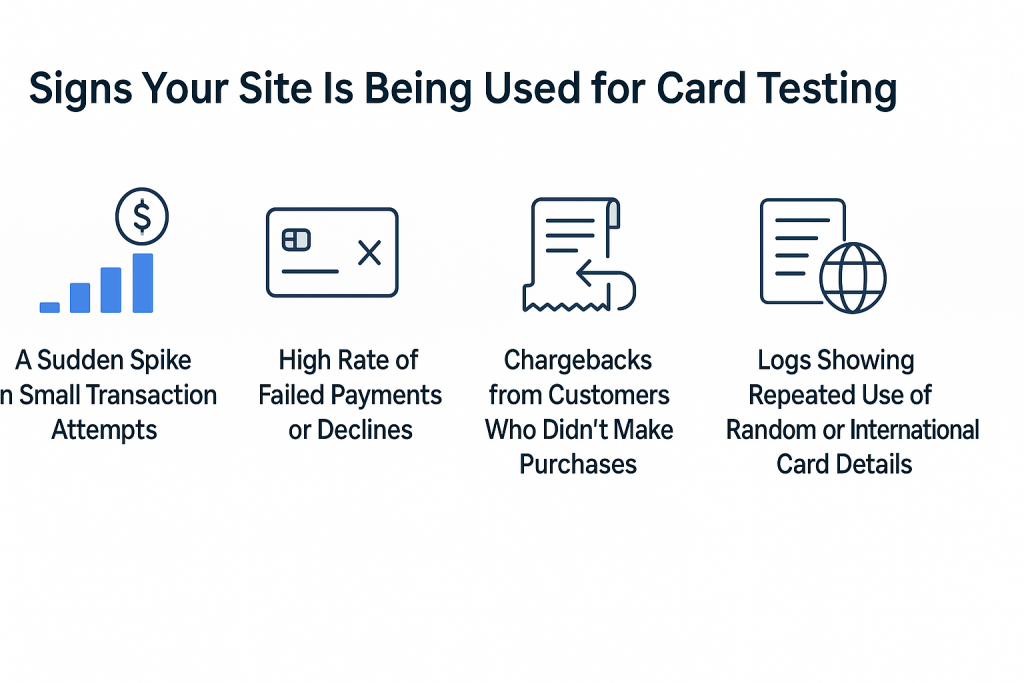
Signs Your Site Is Being Used for Card Testing
Card testing often starts quietly, but it leaves digital footprints you can spot if you know what to look for. Here are the key warning signs.
A Sudden Spike in Small Transaction Attempts
One of the earliest red flags is a sharp increase in low-value transactions, usually $0.50 to $5. These are “test” payments used by bots to verify card activity without drawing attention.
If you notice a wave of small purchases that don’t match typical customer behavior, chances are your site is being targeted. These transactions often fly under the radar if you’re not actively monitoring trends.
High Rate of Failed Payments or Declines
When dozens or hundreds of stolen cards are submitted, most will fail. That creates a sudden spike in declined transactions within a short timeframe.
This puts pressure on your payment processor relationship, as a high decline rate can signal fraudulent activity, even if no real purchases go through.
Chargebacks from Customers Who Didn’t Make Purchases
Legitimate cardholders may notice suspicious charges and file disputes. Even small test payments can trigger chargebacks if the customer didn’t approve them.
Too many chargebacks can ruin your store’s reputation with banks and lead to penalties, withheld payouts, or account freezes.
Logs Showing Repeated Use of Random or International Card Details
If your payment logs show multiple attempts using cards from unusual countries or with random patterns, that’s a red flag. Bots often run through bulk card lists without geographic logic.
Frequent mismatches in billing addresses, names, or IPs are strong indicators that you’re being used as a testing ground, not a real shopping site.
How to Prevent Card Testing Fraud
You can’t stop attackers from trying, but you can make your store much harder to target. Here’s how to block card testing before it causes damage.
1. Add bot challenges and rate limits where you can
CAPTCHA makes automated attacks slower and more expensive for attackers. On Shopify there’s a catch. Shopify’s native checkout bot protection is only available on Shopify Plus. It runs as a scheduled event of up to 60 minutes, is built for flash sales, and Shopify says it isn’t designed to combat bot-related fraud. Shopify’s hCaptcha protects storefront forms, not the checkout itself.
Rate limiting adds another layer by capping how many attempts can come from the same source in a short time. Because bots rotate IP addresses, it’s worth limiting repeated details too (the same email, address or name), not just repeated IPs.
2. Use Fraud Detection Tools
CAPTCHA and rate limits slow bots down, but many card-testing scripts never load your storefront at all. They open a checkout link directly and submit attempt after attempt. A checkout protection app like Blockify adds layers built for exactly that: it blocks bots that skip your store and jump straight to checkout, stops checkouts that reuse the same details too many times within an hour, and lets you set rules for who can complete a checkout.
It works in the background, so real shoppers who browse and buy as usual aren’t affected. You’ll find how each feature works in the Blockify section below.
3. Block Suspicious IPs or Locations
If your store starts receiving payment attempts from countries you don’t serve, or from IPs linked to bot networks, it’s time to block them. Most eCommerce platforms or security tools allow IP filtering and geo-blocking directly from the admin panel.
As a result, you can reduce exposure to bot-based card testing campaigns, which often originate from specific regions or rotate through compromised proxies.

4. Monitor Payment Logs Daily
Regularly checking your payment logs helps you catch unusual activity early, such as sudden spikes in failed payments or repeated attempts from the same user agent. Don’t wait until chargebacks show up to realize something went wrong.
To stay proactive, you should also set up alerts with your payment provider or fraud tool so you’re notified when suspicious behavior is detected, giving you time to react before damage spreads.
5. Use AVS and CVV Matching
Address Verification System (AVS) ensures that the billing address entered by the buyer matches what the card issuer has on file. When paired with CVV verification, this method blocks incomplete or suspicious payment attempts.
Since most attackers don’t have full cardholder data, these checks act as a strong gatekeeper, helping your store reject fraudulent charges before they go through.
6. Remove easy targets
Card-testing bots look for the cheapest or free way to reach payment. Avoid $0 checkout paths, and during an attack consider temporarily hiding very low-priced items or setting a minimum order value.
How Blockify Helps Protect Your Checkout from Card-Testing Bots
Card-testing scripts usually follow two patterns: they skip your storefront and open checkout links directly, and they fire off many checkouts in a short time, often reusing the same email, address, phone number or name. Blockify blocks these bot and repeated-checkout behaviors, cutting off the routes card-testing bots typically rely on. On average, Blockify blocks nearly 100,000 direct-to-checkout bot attempts per store every month.
- Stop bots from creating fake checkouts: Blocks checkouts that don’t start from your store, so bots that jump straight to a checkout link can’t turn it into an order. Real shoppers aren’t affected.
- Stop repeated checkout attempts: Blocks checkouts that reuse the same email, address, phone number or name more times per hour than the limit you set, while the attack is still going on.
- Block Checkout rules: Block checkouts by email, address, country, IP or VPN, and switch on built-in protections such as blocking $0-subtotal checkouts and disposable email addresses.
- Bot blocking on your storefront: Auto-block spam bots and user agent rules turn bots away before they reach checkout, while the Allowed bot list keeps Googlebot and other good bots in.
For setup steps, see how to stop bots from creating fake checkouts and stop repeated checkout attempts.
Real-World Example of Card Testing Attack
In 2022, Stripe, one of the world’s largest payment processors, faced an alarming surge in card testing activity across its platform. Fraudsters were sending millions of low-value or zero-dollar transactions to merchants’ stores, aiming to validate stolen credit card numbers without being detected.
At the height of this wave, Stripe reported that its fraud prevention system, Radar, was blocking over 20 million card testing attempts per day. To help protect merchants, the company upgraded its detection models and urged users to implement stricter anti-bot and payment flow protections. You can read more about how Stripe responded to this threat in their official newsroom report.
What to Do If You’re Under a Card Testing Attack Right Now
- Contact your payment provider. Report the attack and ask whether they can tighten fraud or velocity controls on your account.
- Switch on your strictest checkout protections. Block direct-to-checkout bots and repeated checkout attempts, and turn on $0-checkout blocking.
- Remove easy targets. Temporarily hide your cheapest products or set a minimum order value.
- Cancel and refund successful test orders quickly. A fast refund can stop a test charge from turning into a chargeback.
- Keep a record. Save timestamps, order IDs and screenshots. They help with processor reviews and disputes.
Final thoughts
Card testing fraud may not steal your products, but it can quietly drain your business through fees, chargebacks and a damaged standing with payment providers. Understanding how these attacks work is the first step to shutting them down.
Blockify helps by blocking the behaviors card-testing bots depend on: skipping your storefront to hit checkout directly and repeating checkouts with the same details. Combine it with CAPTCHA, AVS/CVV checks and your payment provider’s fraud tools, and your checkout becomes a much harder target.
Don’t wait for the next spike of failed payments. Lock your checkout down today!
